PowerShell 7.6.7 Is Still Affected by CVE-2026-96251 (CVSS 8.8): The Fix Is 7.6.8 or Newer, and 7.6.9 Is Out

The CVE record for CVE-2026-96251, a PowerShell remote code execution flaw rated CVSS 8.8, lists 7.6.8 as the first fixed 7.6 version, not 7.6.7. That matters because 7.6.7 came out on October 13 alongside the 7.4 and 7.5 fixes, and many admins stopped there. PowerShell 7.6.8 followed on October 22, and 7.6.9, 7.5.13 and 7.4.22 on October 25.
This post shows the release list and the CVE’s affected ranges straight from GitHub and the CVE service, so you can check them yourself, and then gives the versions to aim for. One news article says the October 13 builds fixed the flaw in all three lines. The CVE record disagrees for 7.6, and I explain below which one I trust and why.
Quick guide
- Read your version with
pwsh --version(or$PSVersionTable.PSVersioninside PowerShell). - Compare it to the first fixed version for your line: 7.4.21, 7.5.12 or 7.6.8.
- Update to the newest build of your line, or better, move to 7.6, because 7.4 and 7.5 lose support on November 10, 2026.
- Check the version again after the update.
| PowerShell line | Affected (CVE record) | First fixed | Newest build (Oct 25) |
|---|---|---|---|
| 7.4 | 7.4.0 up to but not including 7.4.21 | 7.4.21 | 7.4.22 |
| 7.5 | 7.5.0 up to but not including 7.5.12 | 7.5.12 | 7.5.13 |
| 7.6 | 7.6.0 up to but not including 7.6.8 | 7.6.8 | 7.6.9 |
The evidence: release dates and the CVE record
These two commands need only curl and jq. The first lists the latest PowerShell releases with their publish times. The second reads the CVE record’s affected ranges:
curl -s 'https://api.github.com/repos/PowerShell/PowerShell/releases?per_page=7' \
  | jq -r '.[] | "\(.tag_name)  \(.published_at)"'
curl -s https://cveawg.mitre.org/api/cve/CVE-2026-96251 \
| jq -r '.containers.cna.affected[]
| "\(.product) first fixed in \(.versions[0].lessThan)"'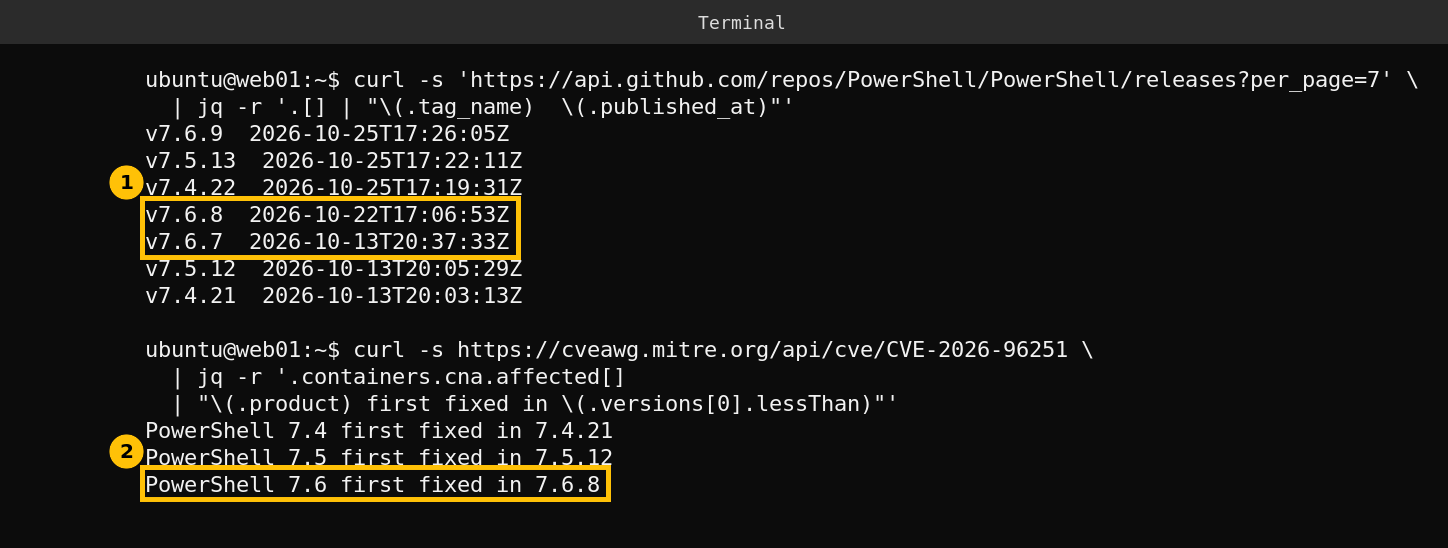
The record is the CVE record filed by Microsoft, and it was published on October 13, 2026. Its description is short: reliance on untrusted inputs in a security decision lets an unauthorized attacker execute code over a network, rated 8.8 under CWE-807. It does not name a cmdlet.
Why I trust the record over the news article
- The article: NTCompatible says the October 13 builds 7.4.21, 7.5.12 and 7.6.7 fixed the flaw, and ties it to
Import-PSSession. I could not find a second source for the cmdlet detail. - The record: the CVE service lists 7.6 as affected up to but not including 7.6.8. That is the data other tools read to flag a vulnerable build.
- The release notes: the GitHub notes for 7.6.7 and 7.6.8 do not name this CVE. 7.6.8 lists one change, removing the Update Notification feature, and 7.6.9 lists only a .NET SDK update.
So I cannot prove from the notes which 7.6 build fixed it. The safe reading is the record’s: treat 7.6.7 as affected, and land on 7.6.9 or newer. Landing on 7.6.9 is correct under both readings.
Update
On Windows, the usual way is winget upgrade --id Microsoft.PowerShell, or the MSI or MSIX from the releases page. On Linux, use the package source you installed from. I do not run PowerShell 7 on this server, so I did not run these update commands and show no output for them. If you are still on 7.4 or 7.5, plan the move to 7.6 now, as I laid out in the 7.4 and 7.5 end of support checklist.
Caveats
I read public records on October 26, 2026 and did not test the flaw. The detail about Import-PSSession comes from a single article. Records can be amended, so recheck the CVE page if you are making a patch decision.
FAQ
Which PowerShell versions fix CVE-2026-96251?
According to the CVE record, 7.4.21, 7.5.12 and 7.6.8 are the first fixed versions of each line. Newer builds of the same line include them.
Is PowerShell 7.6.7 vulnerable?
The CVE record lists 7.6 as affected up to but not including 7.6.8, so 7.6.7 is affected under that record. One news article claims otherwise.
What is the safest version to run today?
7.6.9 was the newest 7.6 build on October 25, 2026. It is also the supported line after November 10, 2026.
Does this affect Windows PowerShell 5.1?
The record I read lists only PowerShell 7.4, 7.5 and 7.6, so I cannot say anything about 5.1 from it.
How bad is it?
The record rates it CVSS 8.8 with a remote code execution impact over a network. It does not describe the attack steps.