October 13, 2026 Was the Last Possible Security Update for Windows Server 2012

October 13, 2026 was the last Patch Tuesday Windows Server 2012 and 2012 R2 will ever receive a security update for, at any price, through any channel. Extended Security Updates (ESU) for these versions were only ever available for three consecutive annual terms after the original end-of-support date in October 2023, and the third and final year closed with this release. There is no fourth year to purchase. If you still have a Server 2012 or 2012 R2 instance running anywhere, it is now permanently unpatched against anything disclosed from this point forward.
What ESU actually covered, and what it never did
It’s worth being precise about what just ended, because ESU coverage was narrower than full support even while it was active. ESU only ever delivered updates Microsoft classified as Critical or Important severity, not the full patch set a mainstream-supported OS receives, and it required a paid license per server (or inclusion in an eligible Azure arrangement) on top of that. Many organizations treated ESU as a bridge to finish a migration, not a permanent home, and that bridge is now gone entirely, not just getting more expensive.
Step 1: find out if you actually have any, don’t assume
This is exactly the kind of thing that survives in an environment because nobody specifically went looking, a forgotten file server, an old line-of-business app nobody wants to touch, a box that “just works.” Check your actual Active Directory, not your mental inventory:
$legacy = Get-ADComputer -Filter {OperatingSystem -like "*Server 2012*"} -Property OperatingSystem
Write-Output ("Server 2012/2012 R2 computer objects found: " + @($legacy).Count)
$legacy | Select-Object Name, OperatingSystem
Real result, run against our own lab domain:
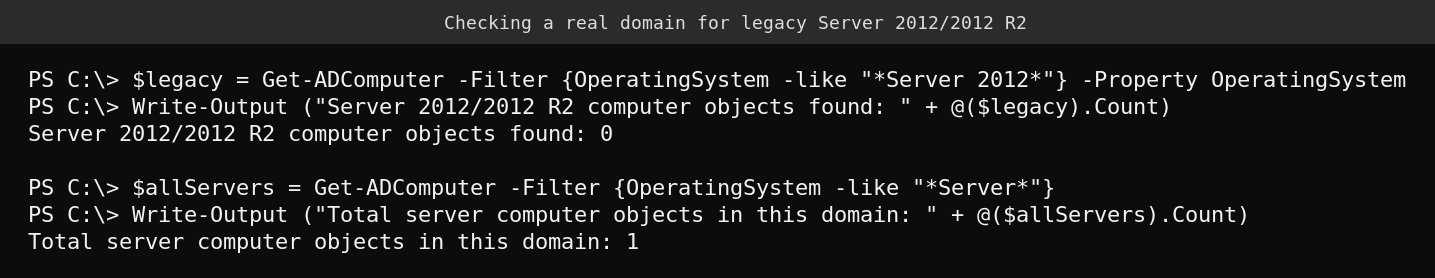
This lab domain has none, which is the clean result you want to see. If your own query returns anything, that’s your actual action list, not a hypothetical one.
A domain-wide AD query only finds domain-joined machines. Also check anything standalone or workgroup-joined (some legacy appliances and line-of-business servers are deliberately kept off the domain), and check your hypervisor inventory directly, a Server 2012 VM that’s powered off most of the time still won’t show up as “currently logged on” in casual checks but is still a real liability sitting in your environment.
Step 2: if you find one, the real options are narrow now
- Migrate the workload to a currently supported OS, this is the only option that actually resolves the exposure rather than managing around it.
- Isolate it aggressively if migration genuinely can’t happen immediately: no direct internet exposure, tightly scoped network access to only what specifically needs to reach it, no interactive logons beyond what’s strictly required. This reduces risk, it does not eliminate it, there is no patch coming regardless of what you do.
- Azure migration is worth checking specifically: Azure has, at various points, offered extended update eligibility tied to running the workload in Azure (via Azure Arc or as an Azure VM) separate from the standalone ESU program. Check current Azure documentation for whether anything like that still applies to your specific scenario, this changes over time and is worth verifying rather than assuming either way.
Step 3: treat this as a prompt to check adjacent old infrastructure too
A Server 2012 box rarely exists in isolation, it’s often paired with an equally old SQL Server instance, an old authentication mechanism, or other infrastructure from the same era that’s worth checking while you’re already looking. Expand the inventory query to a broader version check across your whole fleet while you’re at it, rather than treating this as a one-off search for exactly one OS string.
Get-ADComputer -Filter {OperatingSystem -like "*Server*"} -Property OperatingSystem, OperatingSystemVersion |
  Select-Object Name, OperatingSystem, OperatingSystemVersion | Sort-Object OperatingSystem
Quick guide
- Query AD for any Server 2012/2012 R2 computer objects today.
- Separately check standalone/workgroup machines and your hypervisor inventory, AD alone won’t catch everything.
- For anything found, prioritize migration over isolation, isolation only reduces risk, it doesn’t remove it.
- If migration genuinely can’t happen now, lock down network exposure and access as tightly as the workload allows.
- While you’re checking, run a broader OS version sweep across your fleet, not just this one specific search.
FAQ
Can I still buy ESU for Server 2012 after October 13, 2026?
No. The program was structured as three consecutive annual terms maximum from the original 2023 end-of-support date, and the third year closed with this release. There is no fourth year, at any price, through any purchasing channel.
Will an unpatched Server 2012 box just stop working?
No, it keeps running exactly as it did the day before. What’s gone is any future security patch for vulnerabilities disclosed from this point forward, the exposure accumulates silently over time rather than causing an immediate, visible failure.
Does this affect Windows 8/8.1, the client-side equivalent era?
Windows 8.1 reached its own separate end of support in January 2023 and never had an ESU program at all, so it’s been unpatched for longer already. This specific milestone is about the server OS versions and their ESU program specifically.
Is running it in Azure a way to keep getting updates?
Azure has in the past extended eligibility for certain update programs to workloads running as Azure VMs or connected through Azure Arc, separate from the standalone ESU purchase program. Whether that still applies and what it currently covers is worth checking directly against current Azure documentation for your specific situation rather than assuming, this is exactly the kind of detail that changes over time.